ما هو TISAX وكيف حصلت Spyrosoft على شهادة TISAX


For some time now, the automotive sector has been especially impacted by digitalisation and the wide adoption of software. The days when we expected cars to be able to move us from point A to B, having low maintenance costs are gone. Cars have become multimedia devices in addition to their basic function, driving.
Car manufacturers are rushing to deliver fancier and fancier versions of cars to outrun the competition. The entire development process of a given vehicle model involves the whole supply chain that the Original Equipment Manufacturers (OEMs) collaborate with. The complexity of the automotive supply chain may surprise you: according to publicly available data, one of the German premium car OEMs works with approximately 60,000 direct suppliers worldwide (!).
In such a vast and diverse collaboration model, OEMs must be confident that when sharing their secrets, prototype designs, innovative solutions etc. their suppliers can ensure the highest standards of information protection. One possible way this issue can be handled is to audit all suppliers before entering into cooperation. As much as this can be a very successful method it is used only in selected cases due to high resource and effort requirements.
فتح هذا التحدي الحاجة إلى تعريف معيار أمني خاص بقطاع السيارات يتعين على الموردين الامتثال له – وهو TISAX.
في هذه المقالة، سأشرح ما هي شهادة TISAX وأخبرك كيف تحقق Spyrosoft هذه الشهادة.
TISAX – النشأة والآلية
من أجل وضع متطلبات مشتركة لأمن المعلومات, tailored specifically for the automotive industry in 2017, the German Association of the Automotive Industry (VDA) with the cooperation of OEMs such as Audi, Daimler, Mercedes, Volkswagen, established TISAX® (تبادل تقييم أمن المعلومات الموثوق). لم تحاول هذه المجموعة إعادة اختراع العجلة، بل استخدمت معيار أمن المعلومات القائم بالفعل – ISO/IEC 27001 – متطلبات نظام إدارة أمن المعلومات وأضاف هذه "النكهةAutomotive" الإضافية.
In simple terms, TISAX is an information security assessment and exchange mechanism. This means that the first step for a company that wants to be TISAX compliant is to go through a set of security requirements defined in the VDA ISA catalogue and perform an assessment (first self-assessment and then assessment by an independent third-party audit provider). Once the audit results are positive, an organisation is issued with a TISAX label and the assessment results are exchanged on the ENX platform with other TISAX participants.
What differentiates ISO-based certifications of management systems and TISAX is that in the case of ISO, you get a certificate that you can publish on a website or send to anyone. With TISAX, you do not receive a certificate, but your assessment result information is visible on the ENX assessment exchange portal. If you want (or you are requested) to exchange the details of the assessment information with other TISAX participants (business partner, client, company) you share a copy of that assessment information generated specifically for that unique TISAX participant.
>> تعرّف على كيف يمكننا مساعدتك في تحقيق الامتثال لمعايير قطاع السيارات
TISAX – الهيكل
The TISAX label, or as it is sometimes referred to as the “TISAX certificate”, is not the same for each company but reflects the scope and target maturity of the assessment chosen by an organisation.
ينقسم نطاق متطلبات TISAX في كتالوج VDA ISA إلى 3 وحدات:
Each module, apart from requirements grouped into categories “must” and “should”, defines additional ones – “high protection needs” and “very high protection needs”. This means that we move from basic security protection needs (“must” and “should” requirements) to the most rigorous (“high” and “very high”).
Once we decide which TISAX module is applicable to our organisation or which is required by our business partner, we can choose the target level we want to implement (or our business partner has indicated).
The maturity levels in TISAX, also called Assessment Levels (AL), are not a new idea. They are taken from well-known industry process frameworks such as CMMI or A-SPICE. We distinguish the following ALs in TISAX:
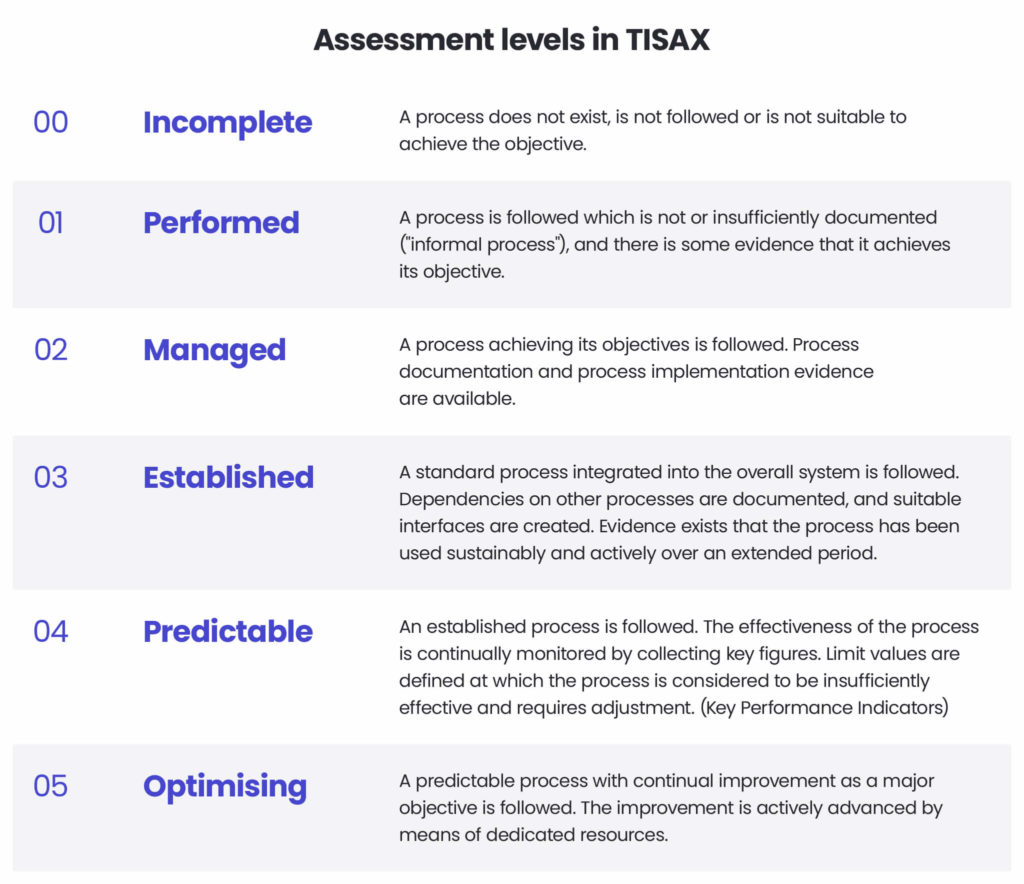
من أجل تحقيق AL3 – راسخ، يجب على المؤسسة تنفيذ جميع المتطلبات المحددة في المجموعات "يجب" و"ينبغي" و"عالية" و"عالية جدًا".
تزداد صعوبة تنفيذ متطلبات TISAX مع مستوى النضج المستهدف الذي تريد تحقيقه. إن معيار صناعة السيارات وتوقعات الشركات المصنّعة للمركبات و/أو الموردين من المستوى الأول هي AL3 – تأسست– which means that the organisation has taken sufficient measures to ensure protection for information assets with high and very high protection needs. Levels 4 and 5 can be utilised internally in the company as part of continual improvement initiatives. However, very rarely does it happen that business partners expect them from their suppliers.
كجزء من أنواع التقييم، تنطبق القواعد التالية:
- ID، – بالنسبة لمستوى ضمان الأمان AL1 في أي وحدة، يلزم إجراء التقييم الذاتي فقط من قبل المؤسسة. ولا يتم التحقق منه من قبل أي طرف ثالث.
- AL1 – for AL2, apart from the self-assessment prepared by the organisation, an independent audit provider needs to be selected (the list of accredited audit providers is published in official TISAX resources). The audit provider gets familiar with the self-assessment results and then performs a plausibility check. Such an assessment usually is performed remotely.
- AL2 – for AL3, both self-assessment and selection of the independent audit provider is required. This type of assessment always takes place on-site, on a company’s premises, in any of its locations that is declared to be aiming at AL3.
ومن المثير للاهتمام أنه إذا كانت المؤسسة تخزّن أجزاء ومكونات نموذجية وتعمل بها، فيجب عليها استيفاء متطلبات AL3 بشكل مباشر على الأقل.
حصلت Spyrosoft على شهادة AL3 TISAX – أمن المعلومات مع احتياجات حماية عالية جداً في مواقع فروتسواف وكراكوف وزغرب.
TISAX في Spyrosoft
We’ve been observing the increasing adoption of TISAX since 2020 and we have been preparing for it ever since. With time, more and more OEMs expected their suppliers to implement TISAX. Today this “expectation” has evolved into a requirement, which means that suppliers without a TISAX label are not considered in quotation requests for new projects.
We started TISAX implementation as an internal project led by the Quality Management department. We made use of the already implemented and certified ISO 27001 Information Security Management System, so in this context, I view TISAX implementation not as another new standard to follow, but as an improvement of our already established policies and procedures.
Although TISAX is associated with the automotive industry, it is not sufficient to implement it only in the Automotive Business Unit. The general idea is that the whole system (or all company departments) must be aligned so that the same level of protection is provided regardless of where a given information asset is processed.
>> سرّع وقت الوصول إلى السوق من خلال خدمات هندسة المنتجات لدينا
ما هي الفوائد التي يقدمها TISAX؟
يمكن تقسيم الفوائد إلى فئتين.
داخلي:
- تحسين عمل نظام إدارة أمن المعلومات الحالي (وبشكل أكثر تحديدًا سياساته وعملياته وإجراءاته)
- زيادة الوعي الأمني لدى الموظفين
Eخارجي:
- زيادة ملحوظة في طلبات عروض الأسعار للمشاريع الجديدة
- تدقيق/مراجعات أمنية أقل كثافة يقوم بها العميل عند إعداد المشروع
The last point perfectly sums up the overall TISAX philosophy – “Since you are TISAX certified, I know what security measures you had to implement to achieve that, so I’m confident my data will be handled with the highest protection standards.”
Formally, TISAX certification is not fixed for an unlimited period. As it is with any company-wide-management system, it needs to be alive, maintained, improved on, and periodically checked for compliance. In three years’ time, we will be undergoing an external re-assessment for the renewal of our TISAX labels.
نحن لا نبطئ الوتيرة وقد بدأنا بالفعل تنفيذ TISAX في مكتبنا في تيميشوارا، رومانيا.
arrow_circle_rightاتصل بنا
سنساعدك على تطبيق معايير السلامة في قطاع السيارات

arrow_circle_right مقالاتنا




